
AWS Continuum explained: AI vulnerability validation and fix PRs
AWS Continuum is generally available: it builds a context graph, tests exploitability in a sandbox and opens fix pull requests. How Learn and Enforce work.
2 min read
In this article
AWS Continuum for code vulnerabilities became generally available on 22 October 2026. It builds a context graph of your AWS environment, tests whether suspected vulnerabilities are exploitable in an isolated sandbox, ranks them by business impact, and opens remediation pull requests.
It starts in Learn mode, where you approve every proposed fix. Enforce mode, where it acts within your guardrails, is optional. Its accuracy and fix quality are AWS's claims until you measure them on your own code.
Sources checked on 26 October 2026. Dates, availability and vendor figures can change; confirm the linked primary sources before acting.
How AWS Continuum works
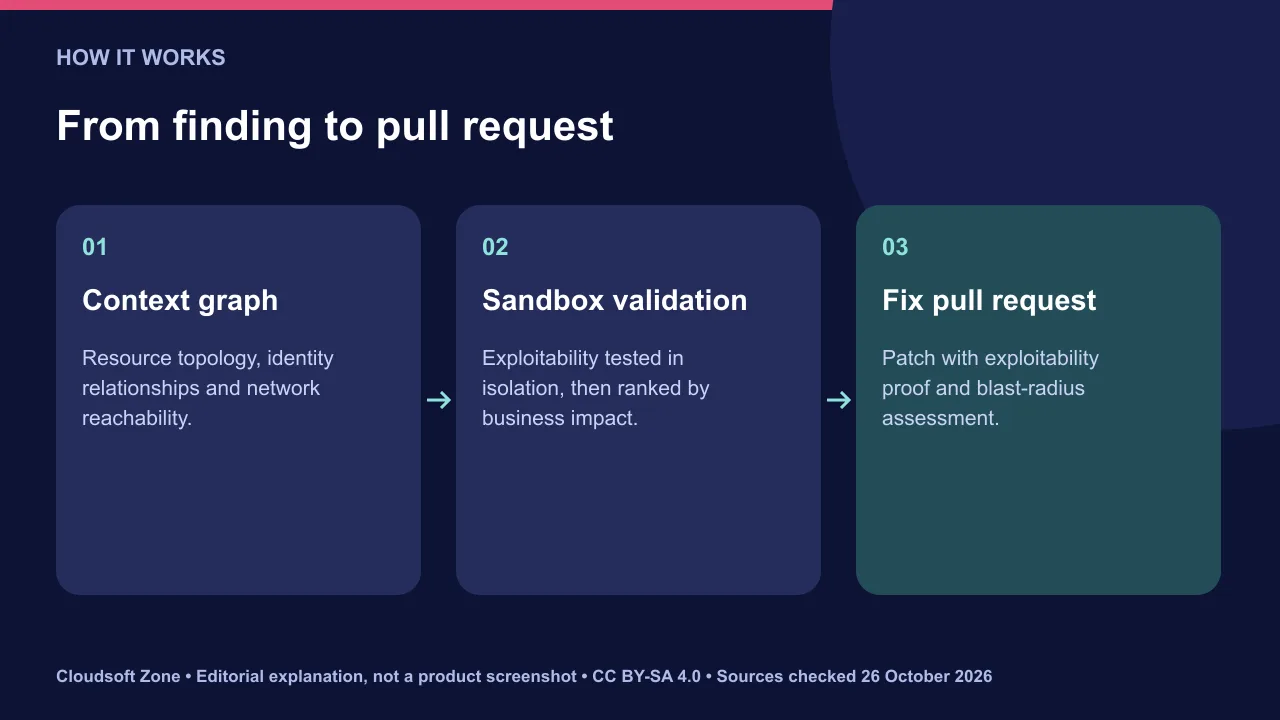
Continuum combines code findings with how your infrastructure is actually wired. The context graph covers resource topology, identity relationships and network reachability.
A finding is then tested in an isolated sandbox to confirm whether it can be exploited. Fixes arrive as pull requests with the exploitability proof and a blast-radius assessment attached. AWS says it picks an AI model suited to each task.
Validated findings vs another CVE list
Most scanners report what might be vulnerable. Continuum's pitch is to report what is reachable and exploitable in your environment.
| Question | Typical scanner | AWS Continuum |
|---|---|---|
| Is the vulnerable code present? | Yes | Yes |
| Is it reachable in this environment? | Rarely | Uses the context graph |
| Is it exploitable? | No | Tested in a sandbox |
| What is the impact? | Severity score | Business impact and blast radius |
Fewer, better-evidenced findings can cut triage time. Keep your existing scanners running while you compare results.
Learn mode first, Enforce mode later
Run Learn mode until you trust its precision on your code. Every fix is a proposal you approve.
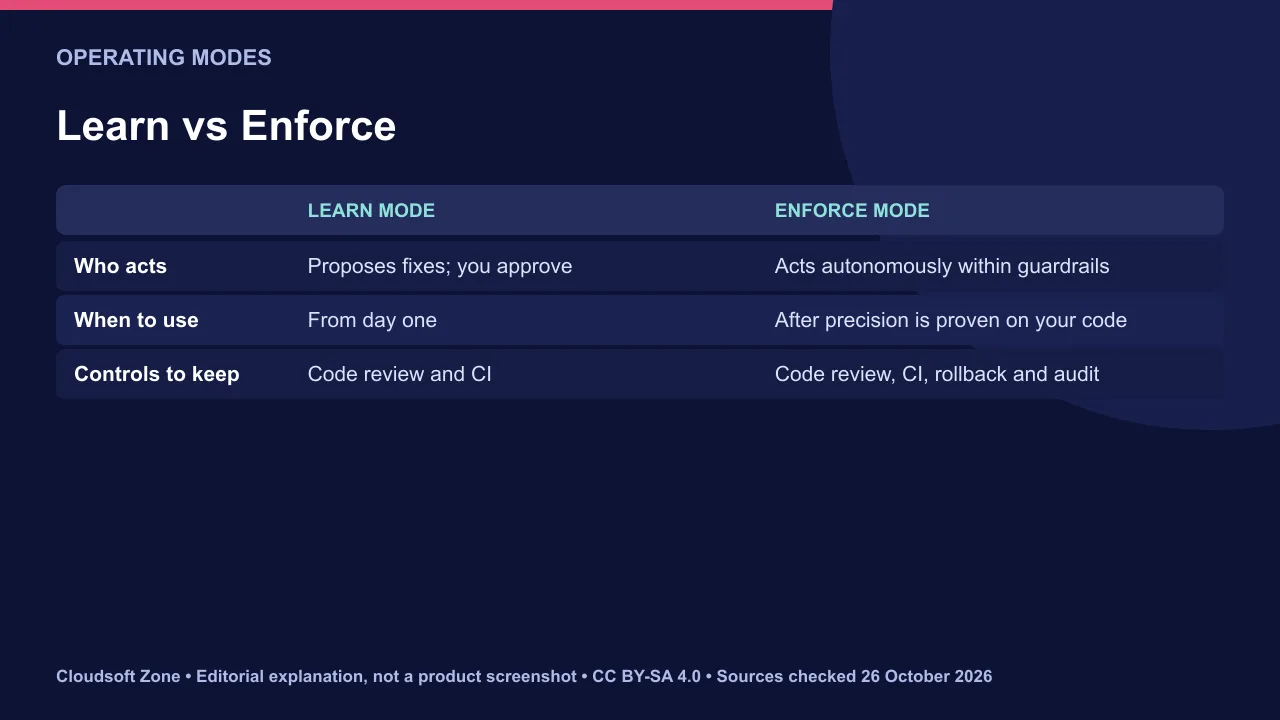
Move to Enforce mode only for repositories with strong tests and fast rollback. Even then, keep code review, required CI checks and an audit trail. An automated fix that passes tests can still change behaviour.
What AWS has not published yet
The announcement does not list supported languages, code hosts or pricing. Regional availability is in the AWS Region table.
Confirm those for your stack before planning a rollout, and check what data leaves your account during sandbox validation.
Our verdict: promising for teams drowning in unvalidated findings; pilot it in Learn mode on one service and compare with your current scanner. For an AWS security assessment or DevSecOps pipeline, see our cloud setup and maintenance services. Related: our code review checklist.
Sources and further reading
Image credits
Explanatory diagrams: Cloudsoft Zone, CC BY-SA 4.0. Featured photograph: Tony Webster from Minneapolis, Minnesota, United States, CC BY 2.0, via Wikimedia Commons. AWS servers in Ashburn, group 1, 2020-10-09 1: Vahurzpu, CC BY-SA 4.0, via Wikimedia Commons.
Frequently asked questions
Does AWS Continuum merge fixes automatically?
Not in Learn mode, where you approve each fix. Enforce mode can act within guardrails you set; keep code review and CI either way.
Which languages does AWS Continuum support?
The announcement does not list languages or code hosts. Check the AWS documentation for your stack.
How much does AWS Continuum cost?
Pricing was not in the general availability announcement. Check the AWS pricing page before a pilot.
Your next customer could start right here.
Introduce your tool, product or business to readers exploring technology.
Explore placements and request a private quote
Sources
- AWS Continuum for code vulnerabilities is now generally available — AWS, 2026-10-22
Written with substantial AI assistance. Facts checked against cited sources. Editorial policy.
Comments
No comments yet. Be the first to join the conversation.
Leave a comment
Every comment is read by a moderator before it appears. Your email address is never published; it is used only to contact you about this comment.
More from Cloudsoft Zone
Troubleshooting guideDevOps
Laravel queue jobs not processing: trace Redis, Supervisor and Horizon
Diagnose Laravel queue jobs not processing without deleting queued work: trace dispatch, connection identity, worker ownership, failures and the business effect.
By Cloudsoft Zone
Troubleshooting guideDevOps
Laravel scheduler not running: trace cron, task filters and execution
Diagnose a Laravel scheduler not running by separating cron invocation, runtime configuration, due-task filters, cache locks and the task’s final effect.
By Cloudsoft Zone
TutorialDevOps
Laravel production deployment: from a Git commit to the first live release
Plan a Laravel production deployment from a reviewed Git commit through dependencies, shared storage, configuration, nginx routing and first-release acceptance.
By Cloudsoft Zone